DPDP Compliance Assessment and Advisory Services
Geopits assesses where personal data is stored across your databases and checks whether it is protected as required by the DPDP Act. Within 2 to 4 weeks, the organisation receives a personal data inventory, a risk-scored gap report and a prioritised roadmap to close each gap.
Why DPDP Compliance Depends on the Database ?
Most organisations have started implementing DPDP with privacy notices and consent banners. The Digital Personal Data Protection Act, 2023 goes further. It asks five questions that only the data layer can answer.
Where is our personal data?
A clear record of where data is held, like production, replicas, backups and test environment.
Is it protected?
Reasonable security safeguards, including encryption, masking, and least privilege access
Who accesses it?
The access log needs to be maintained for at least one year through audit settings, log retention and access alerts.
Can a breach be reported on time ?
A detailed report to be given to the Data Protection Board within 72 hours.
Do we delete data on time?
Erase data when consent is withdrawn, through retention and purge activities.
What We Assess
Personal data discovery
Every table holding names, phone numbers, emails, Aadhaar, PAN & other sensitive information.
Encryption
Ensure encryption at rest, in transit, and in backups and identify the gaps.
Access control
Privileged and shared accounts, least privilege, dormant logins.
Audit and monitoring
What's logged, how long logs are kept, alerts on unusual access.
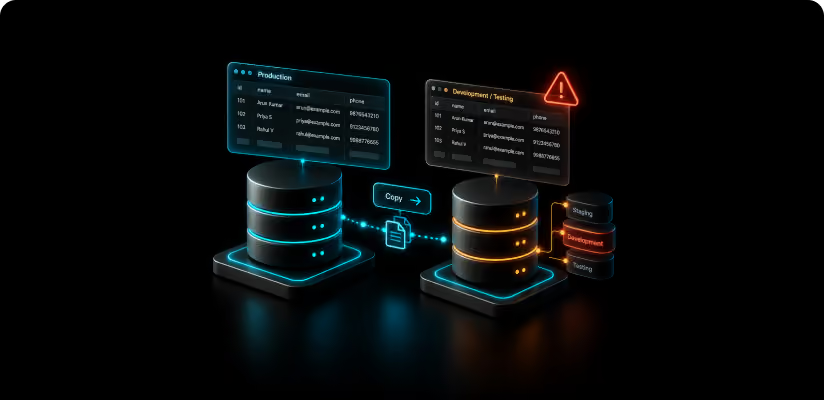
Test and dev data
Real customer data sitting in non-production copies
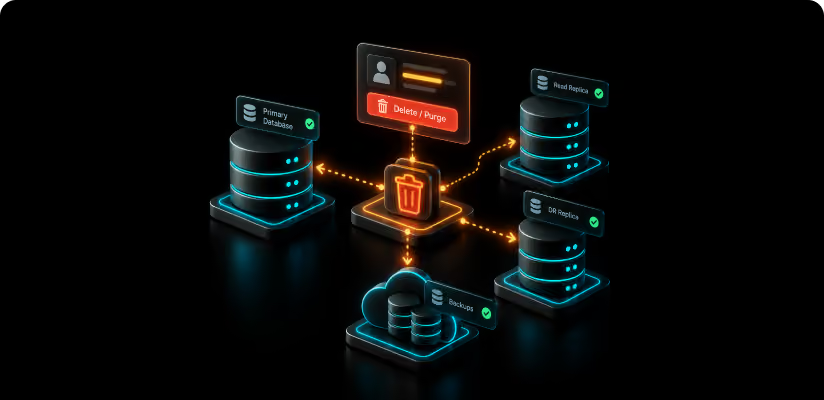
Retention and erasure
Purge and deletion across replicas and backups
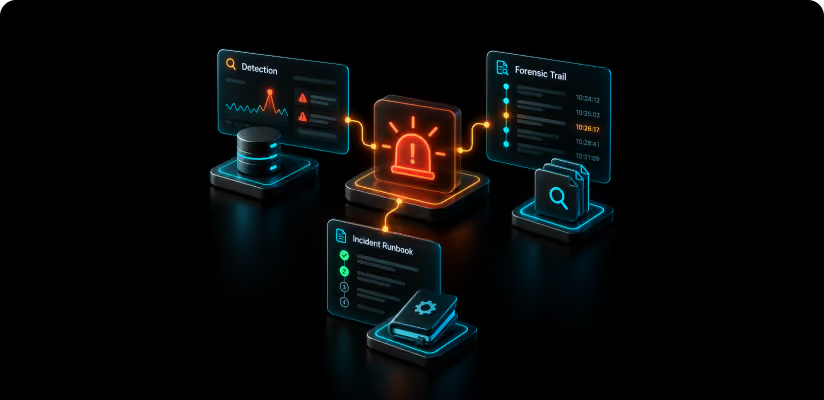
Breach readiness
Detection, Forensic trail, Incident runbook
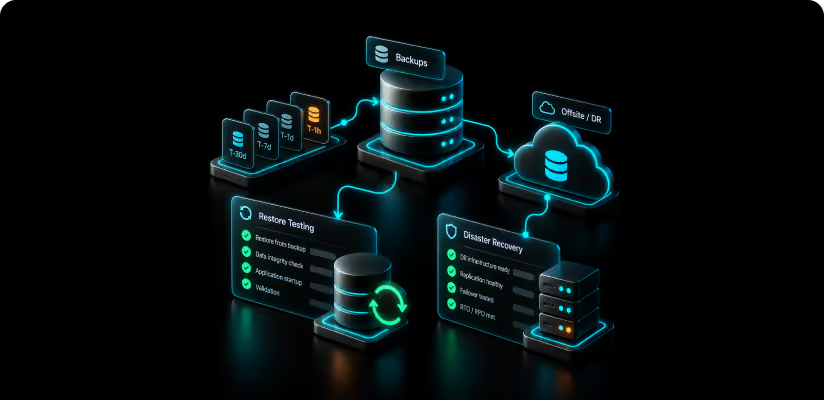
Backup and recovery
Restore testing and DR coverage
How it works
Kickoff (Day 1-2)
We agree the scope and set up secure, read-only access.
Discover (Week 1)
We scan and classify personal data across your databases.
Assess (Weeks 1–3)
We review security controls against DPDP safeguards
Report and Roadmap (Weeks 2–4)
We walk you through the findings and a prioritised plan.
What you get

A personal data inventory across all your databases

A risk-scored gap report (High / Medium / Low)

A prioritised remediation roadmap

A one-page executive summary for leadership

A walkthrough session and implementation plan
Frequently Asked Questions
When does DPDP compliance become mandatory?

Most core obligations apply from around May 2027. Fixing gaps takes months, so it's best to start now.
We already have a privacy policy. Isn't that enough?
A policy says what you'll do. The Act expects you to actually protect, log and delete personal data, and much of that happens in your databases.
Will this affect our production systems?
No. We use read-only access and schedule the work around your peak hours.
Does our data leave our environment?
No. We record only metadata, such as table and column names, never customer records.
What happens after the assessment?
You can act on the roadmap with your own team, or let Geopits handle remediation and ongoing management.
2027 is closer than it looks. Start with a free health check.
A 30-minute call with a senior Geopits Engineer to review your organisation’s database setup and discuss where DPDP gaps are most likely to sit. No obligation.
The privacy policy is the promise. The database is the proof. Geopits gets that proof ready before the Data Protection Board comes asking.